Health systems and hospitals face unprecedented cybersecurity challenges. In May 2016, 89% of healthcare organizations included in a study by the Ponemon Institute had experienced at least one data breach over the prior 24 month period. And, The U.S. Department of Health and Human Services Office for Civil Rights website indicates that health organizations—hospitals, health systems, medical centers, physician’s offices, and healthcare companies—have reported 449 data breaches in just the last 24 months.
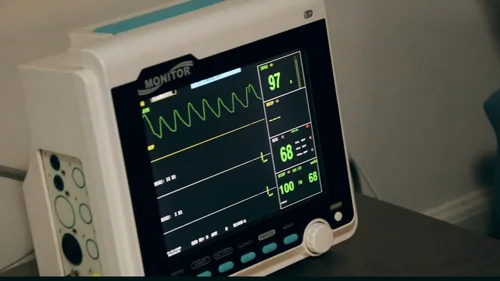
In addition to worrying about data breaches, provider organizations need to think about attacks on their medical devices. Why? Because more and more medical devices are connected to the Internet. Connected medical devices offer many exciting benefits such as remote patient monitoring, automated dose adjustments, “smart” implants, and simpler imaging file transfers. But, they also create countless security problems.
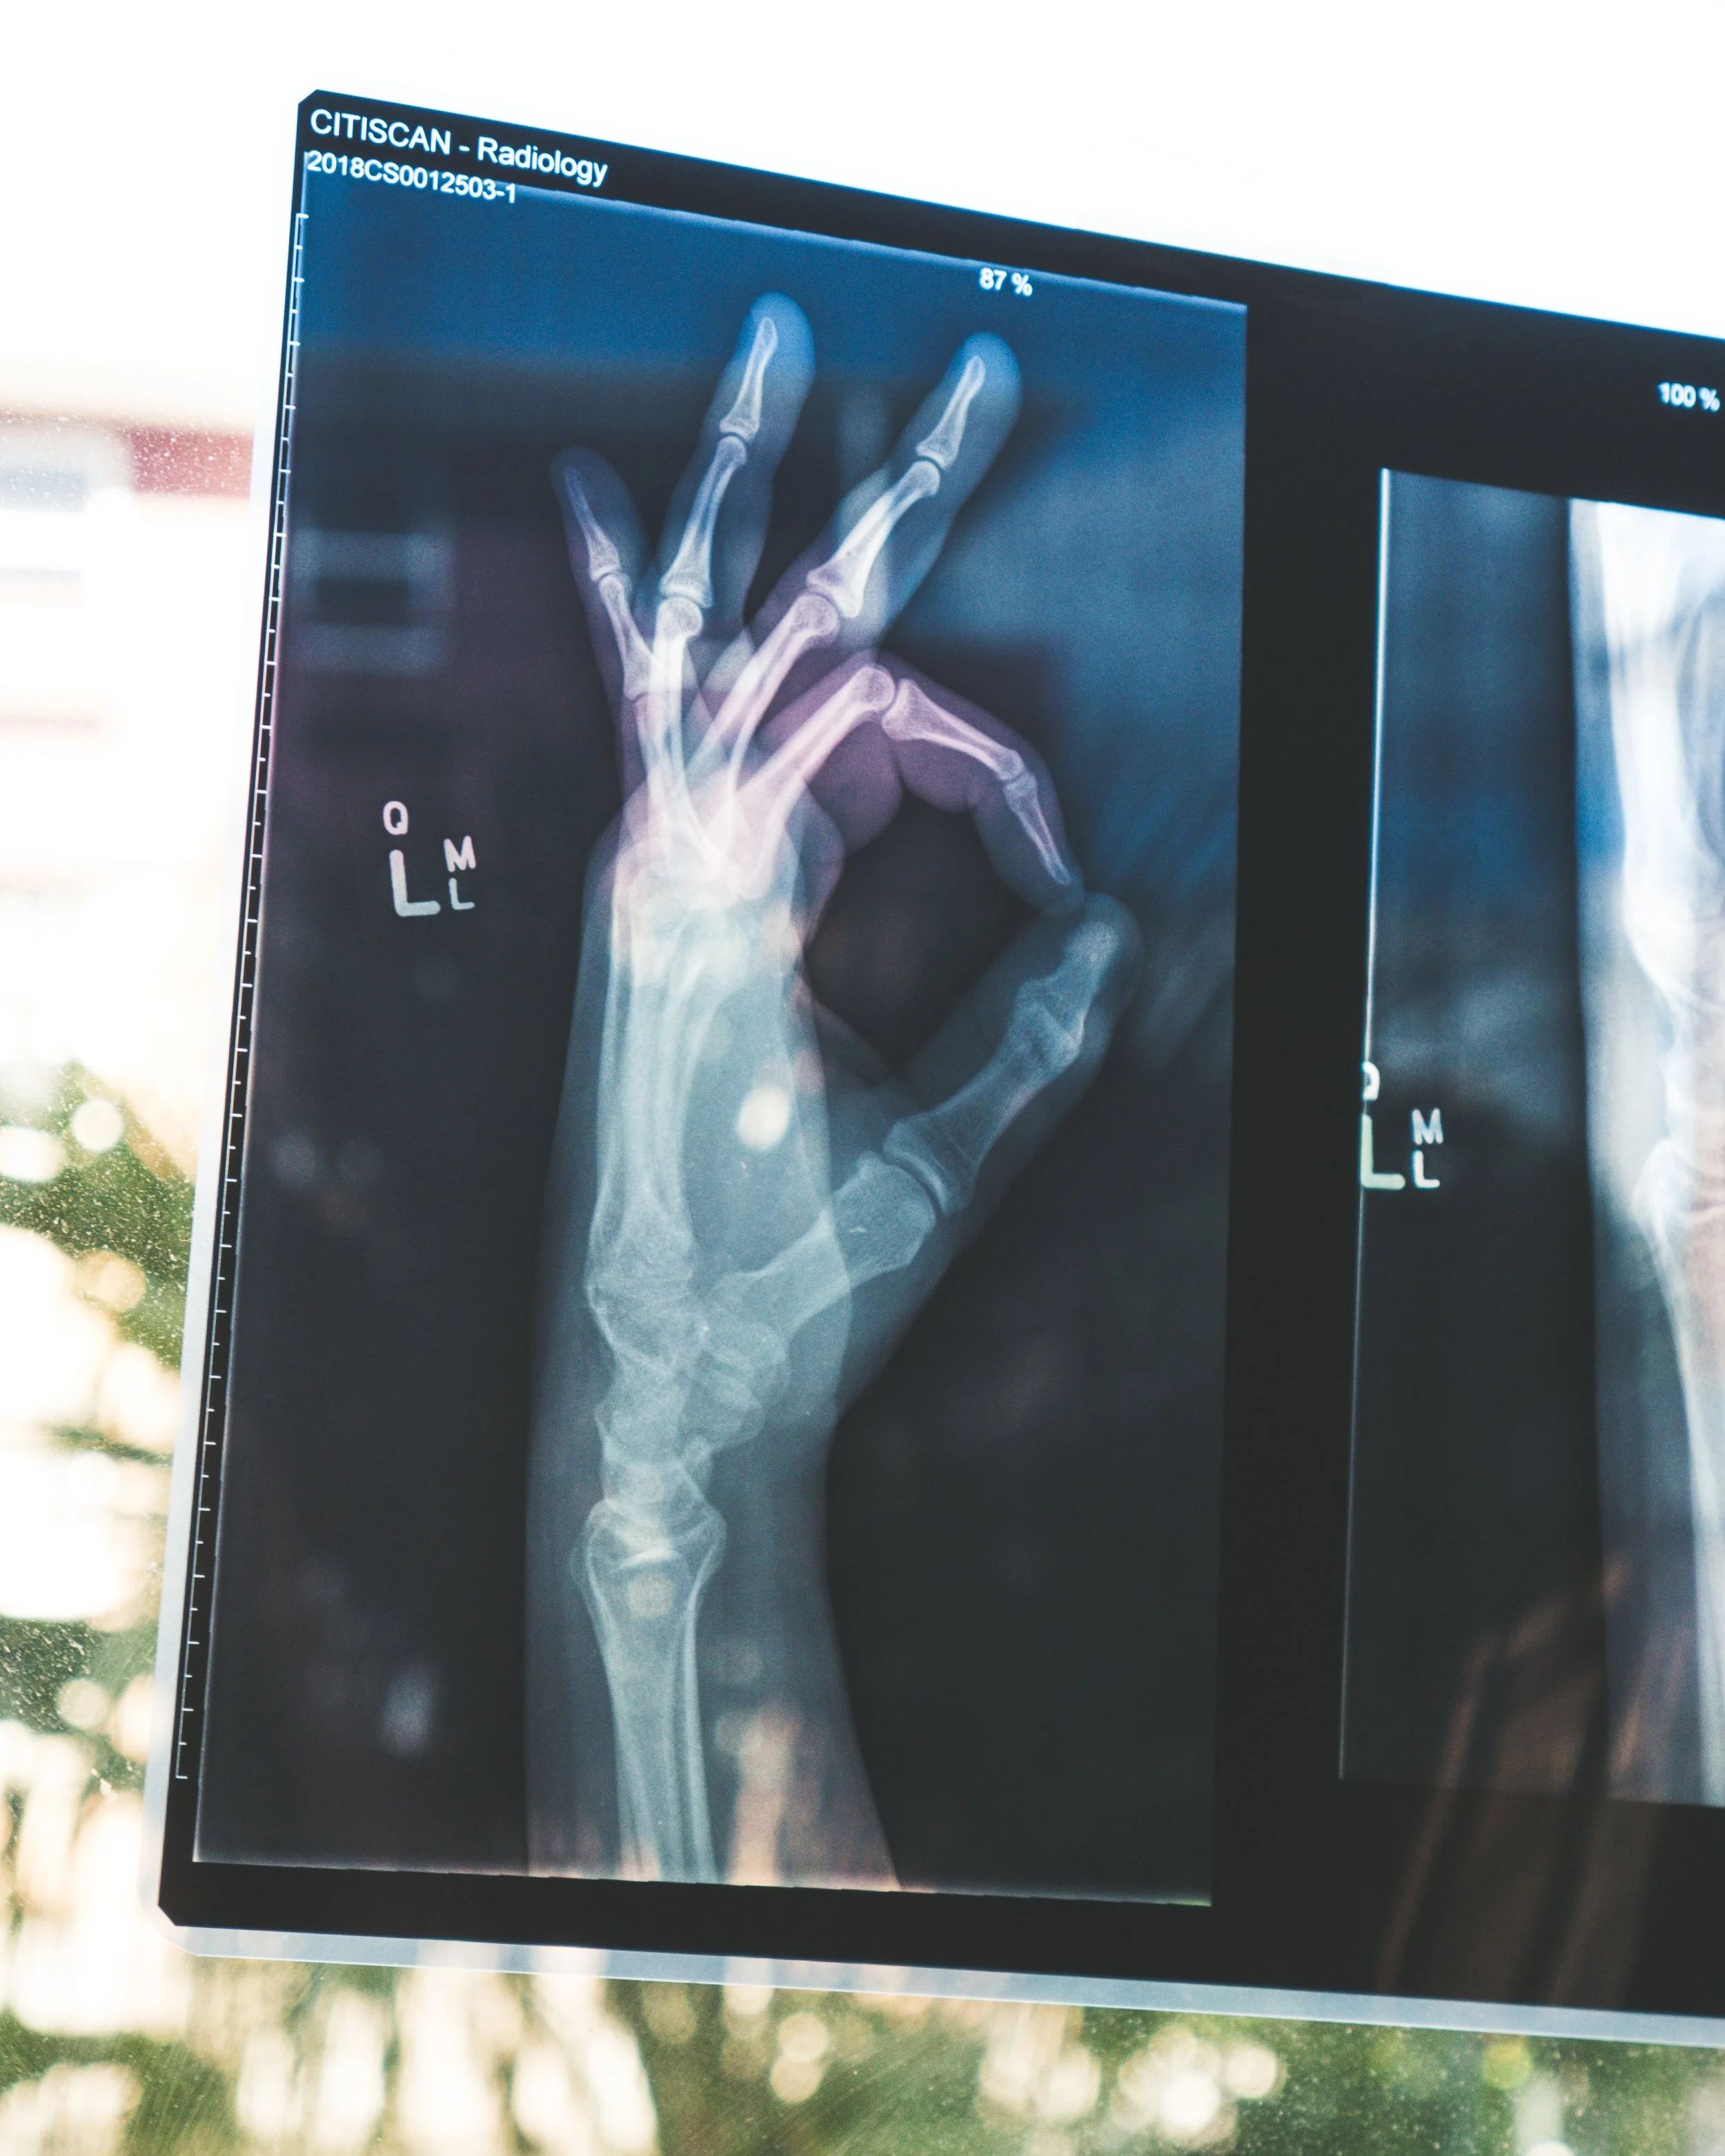
The average bed in a U.S. hospital uses between 10 - 15 connected medical devices. These devices are a real threat to the health of the patient in each bed, the health of all of the patients in the hospital, and the hospital’s entire network. Just imagine if a connected device gets compromised and delivers a toxic dose of insulin or adds malignant-looking growths to a healthy CT scan—that would be a disaster. Now, imagine one of those scenarios happening with tens of thousands of medical devices—the damage would be catastrophic.
In response to these growing threats, several startups have created products to protect connected medical devices. And, in this article, you’ll get a look at the important work that they’re doing.
67% of the medical device manufacturers who participated in a May 2017 study believed that hackers would attack at least one device they had built in the next 12 months. Just 17% of the device manufacturers included in that same study were “taking significant steps to prevent attacks.”
Connected medical device makers have a responsibility to protect their products from cyber threats. Yet, too many companies in the space haven’t prioritized security.
How do we know that manufacturers haven’t made security a priority? 39% of device manufacturers who participated in the study mentioned above said they could confirm that hackers had taken control of their products at some point.
To solve these problems and make medical devices safer, several companies have created tools that allow device makers to add security features to their products. Here’s a look at the most promising startups in this space:
Medical device makers aren’t the only group with responsibility for preventing cyber attacks on their products. Health systems, hospitals, and other healthcare delivery organizations have to be accountable here as well.
Hospitals have tens of thousands of medical devices in their buildings, and most of them are connected to the Internet in some way. Each device presents an opportunity for a hacker to gain access to the entire hospital’s system, meaning an attack on one device presents a threat to every other device, computer, and server on the network.
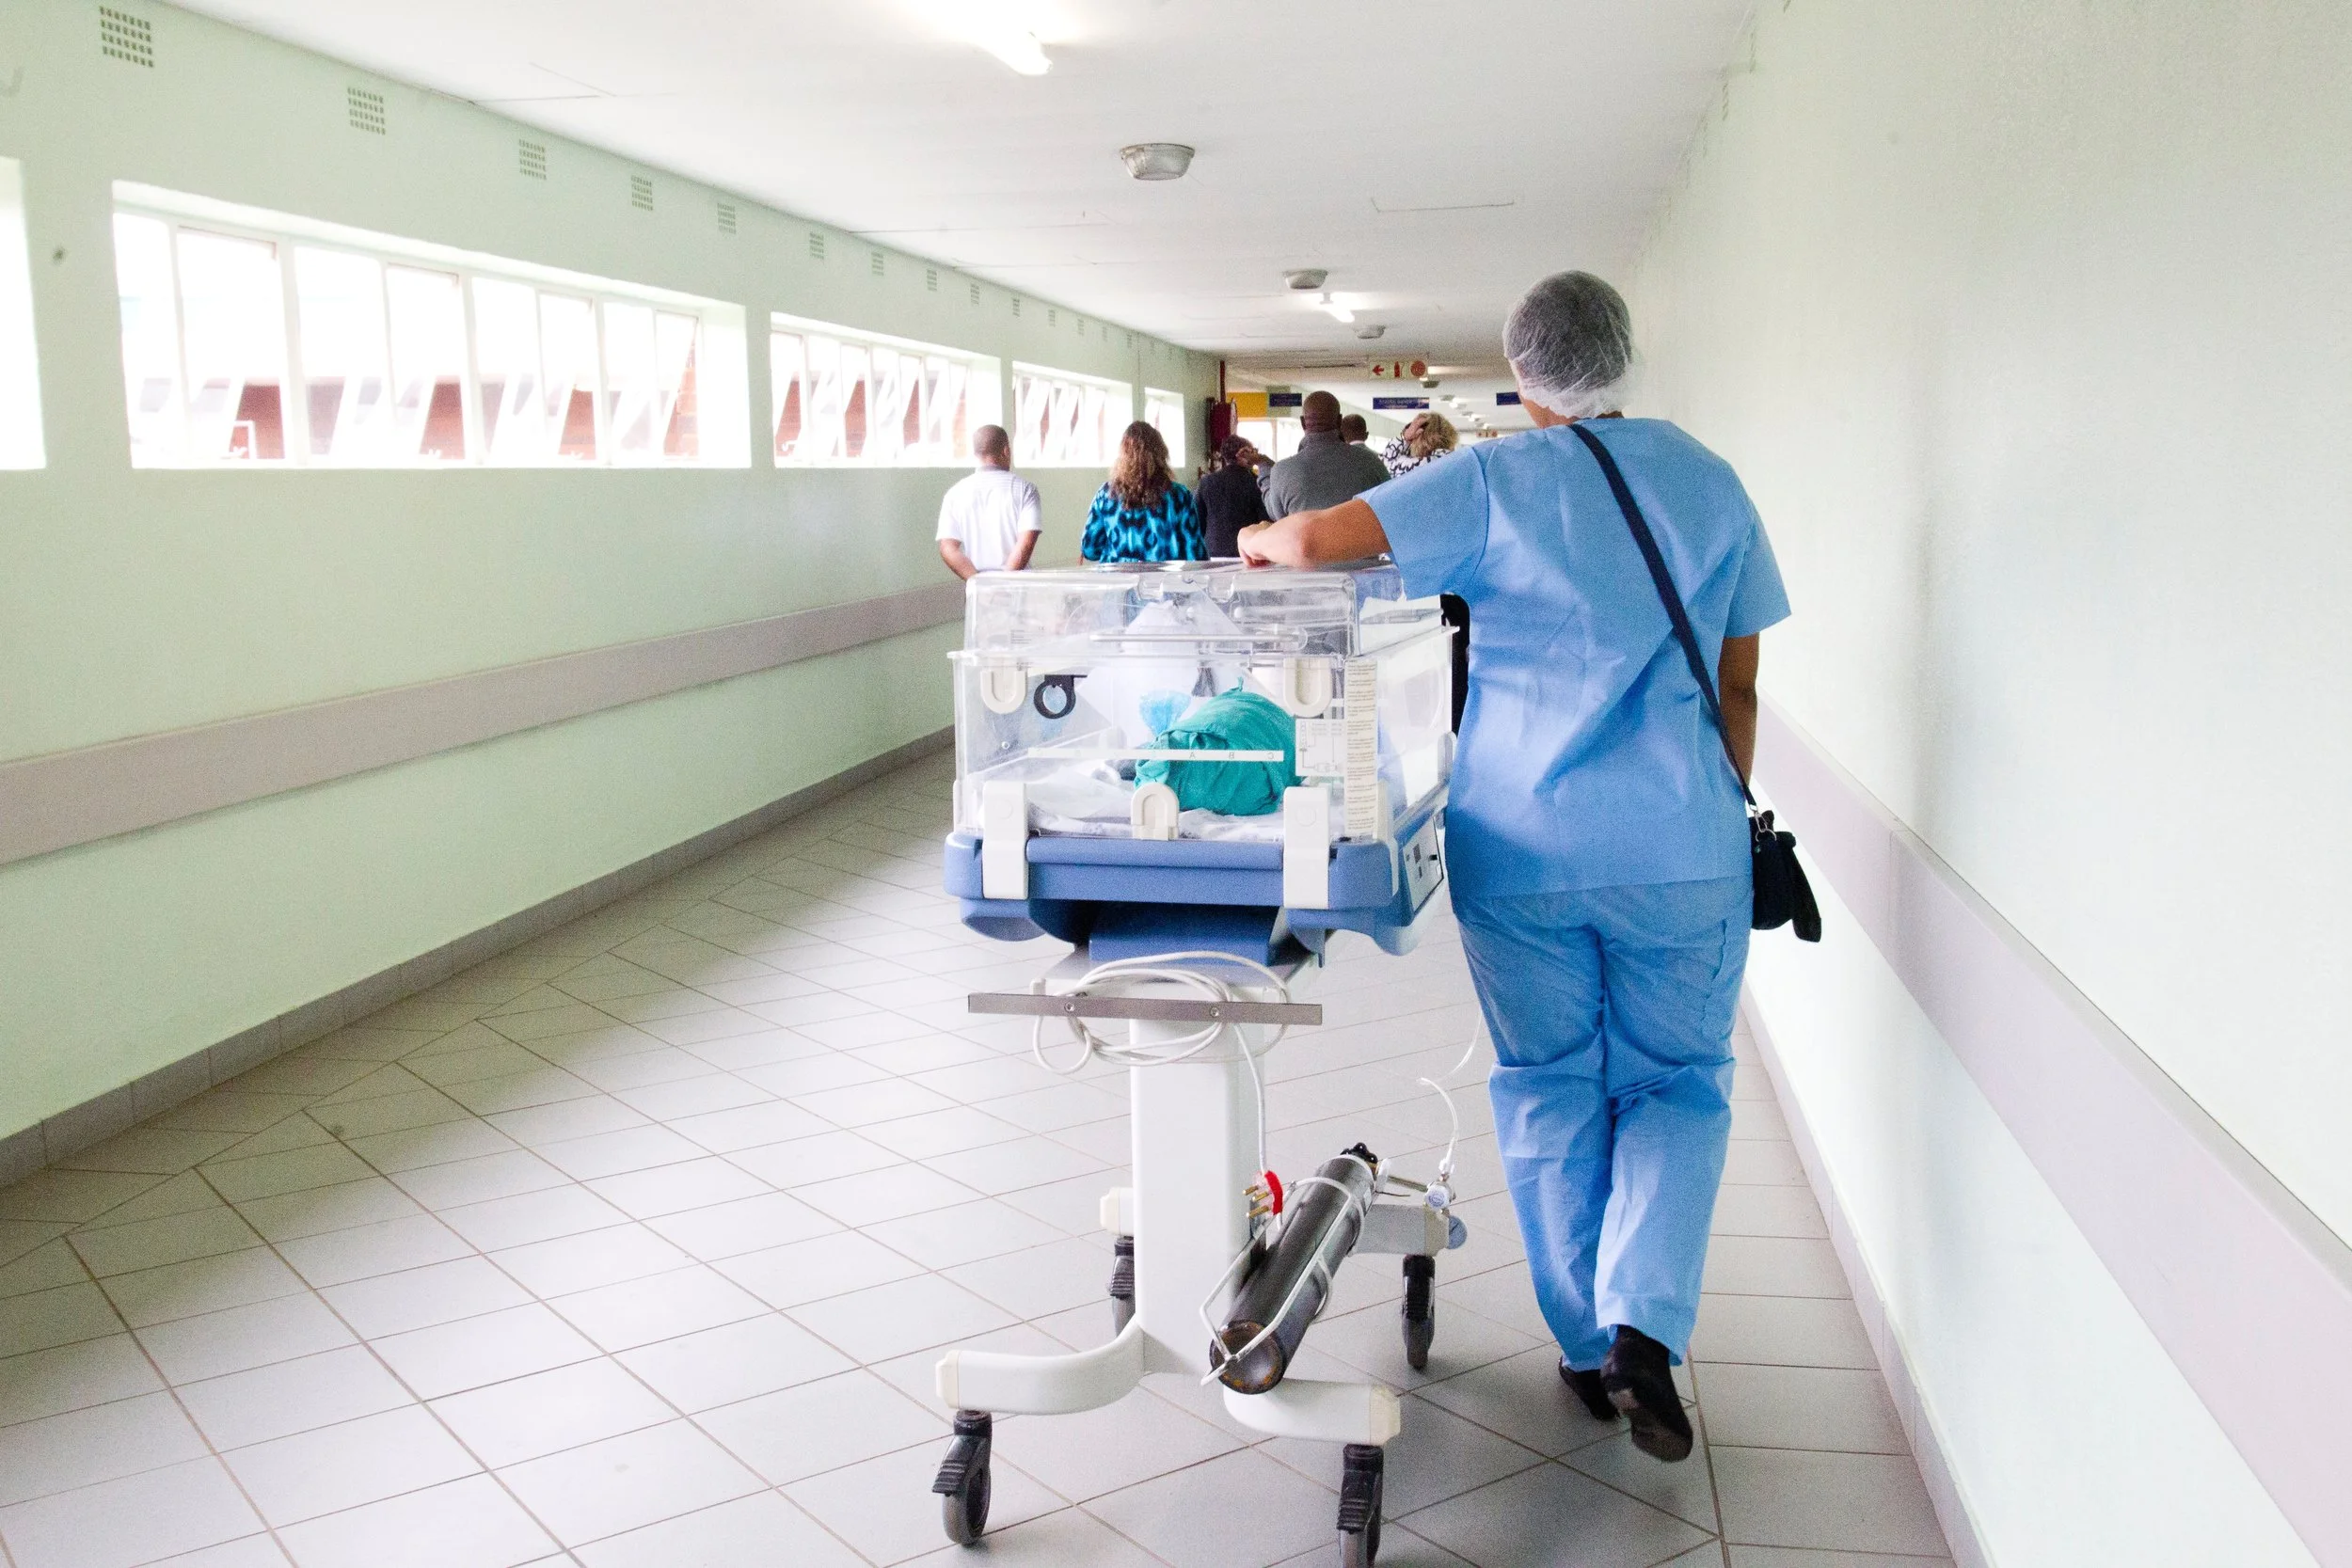
Hospitals and care delivery organizations can’t afford to suffer large-scale medical device hacks. For that reason, many startups have emerged to help them track all of the devices on their networks and stop attacks in their tracks.
Cylera is an innovative startup in this space. It protects against medical device cybersecurity attacks by analyzing health systems’ and hospitals’ networks to identify and categorize the devices on them. With this information, it looks for vulnerabilities, identifies breaches, and protects against threats in a way that doesn’t interfere with device performance or patient health.
Cynerio is another startup that wants to secure connected medical devices by giving providers visibility into the devices that are on their networks, detecting anomalies, and stopping attacks. The company plans to accomplish these goals by constantly monitoring the behavior of providers’ connected medical devices.
CyberMDX is an Internet of Medical Things (IoMT) cybersecurity company with an interesting solution. Its product enables providers to discover and track the IoMT and IoT devices on their networks, assess each device and the overall network for risks, and contain threats from a centralized dashboard.
This sector has gotten quite crowded, and other startups in it that deserve an honorable mention include:
You now have a better understanding of how different cybersecurity startups plan to protect medical devices from intrusions. But, to fully grasp the competitive landscape, you need to look at each company’s funding.
That’s why our team compiled the funding data and investor list for each startup mentioned in this piece. As you’ll see, several companies have raised tens of millions of dollars, and one company has secured more than one hundred million dollars in venture backing. Check out the Airtable database below to see how medical device cybersecurity startups stack up in terms of their funding:


